IAM and RBAC
Updated May 26, 2022 ·
Overview
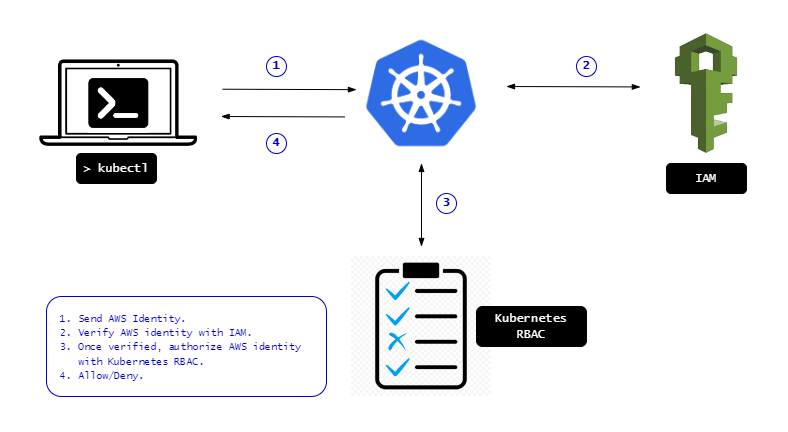
Kubernetes integrates seamlessly with IAM for authentication and RBAC for authorization:
- IAM handles authentication.
- Kubernetes RBAC manages authorization.
IAM entities can be directly assigned RBAC permissions to access Kubernetes clusters.
Worker Nodes
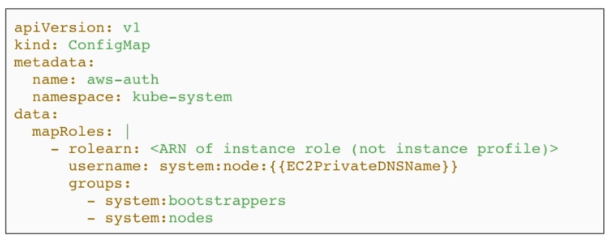
Worker nodes join the cluster with an IAM role mapped to RBAC groups, allowing them to connect:
system:bootstrappersfor initial setup.system:nodesfor ongoing operations.
To edit the configuration, modify the aws-auth ConfigMap:
kubectl edit -n kube-system configmap/aws-auth
IAM Users
Examples of IAM roles and permissions:
- Cluster admin: Full administrative privileges.
- Read-only user: Restricted to specific namespaces.
For more information, please see Using RBAC Authorization..